Most security experts go deep in one layer. I connect them. I've built, defended and assessed security across the stack, from device to network to cloud. MKR Labs brings that depth to where it matters most now, the firmware, radios and hardware inside connected products.
Track record
Telenor
Built and exercised SOC tooling (network intrusion detection and incident handling) at national-operator scale, and operated the DDoS-mitigation defences against live attacks. Worked as a security analyst on the same systems, threat hunting that uncovered malvertising campaigns and zero-day exploits used against our customers in the wild.
Norman Shark
Architect and core developer of a next-generation malware-analysis sandbox, acquired by Blue Coat. Designed and implemented the VM orchestration, VM image customisation, the secured network plumbing around the guests, and the host-to-VM communication, and tuned the Linux host OS for scale. Co-authored threat research that uncovered a state-affiliated hack-for-hire operation.
Blue Coat / Symantec / Norton
Technical Director for the development and cloud deployment of automated dynamic malware analysis, in the Office of the CTO of one of the world's largest security companies. During a major corporate carve-out, helped separate large and complex codebases, identifying shared components and dependencies, and shaping the transition service agreement.
Crosspoint Labs
Technical due diligence and prototyping for a security-focused private-equity firm, assessing products, codebases and engineering teams on the investor's side of the table. Hands-on hardware security research in the same role, assessing a range of consumer IoT devices, reverse engineering UEFI modules, and LTE research into detecting fake base stations. From 2025 the team moved into RSA Conference, helping build a platform to support the cybersecurity community.
MKR Labs
Independent practice. Product security assessments and original research in RF and hardware security.
Why independent
MKR Labs is not tied to any vendor, product or certification scheme, and doesn't do checklist audits. Every engagement starts with a concrete technical question and ends with something you can act on. A finding, a proof-of-concept, a remediation roadmap. Being small is part of the offer. The person who scopes the work is the person who does it and the person who signs the report.
The lab
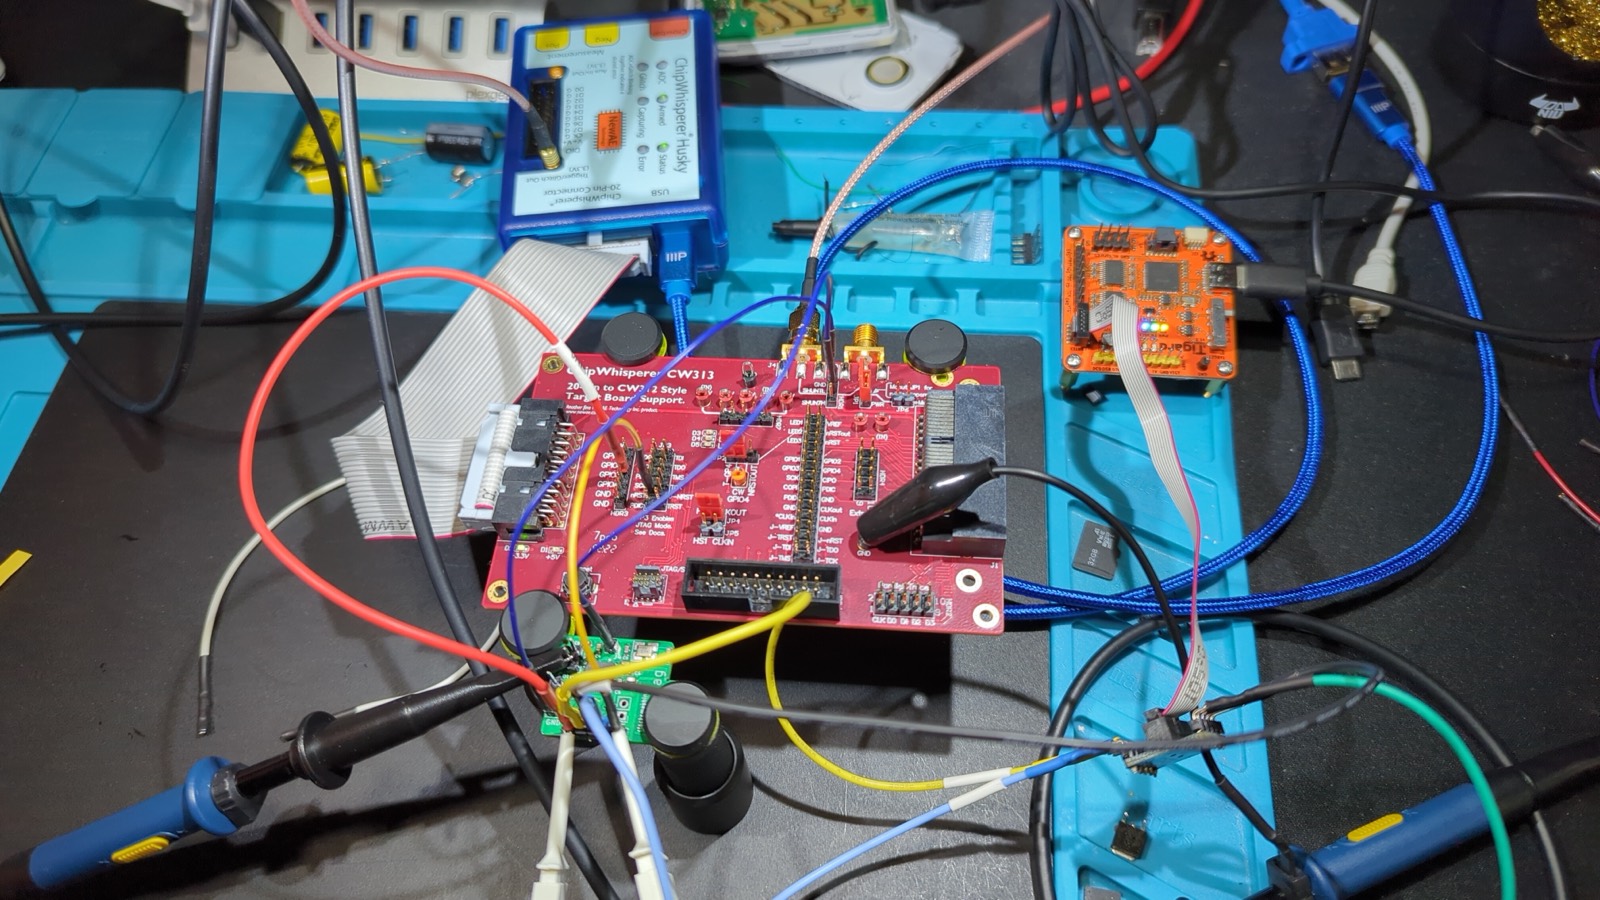
The practice runs on its own equipment. Software-defined radios covering 70 MHz–6 GHz with GPS-disciplined timing, a hardware bench for flash extraction and rework, JTAG/SWD debug tooling, and a ChipWhisperer Husky for fault injection and side-channel work. When an engagement calls for something that doesn't exist off the shelf, the lab builds it, custom rigs made to answer one client's specific question. The assessments come out of that lab, and so does the research behind them.